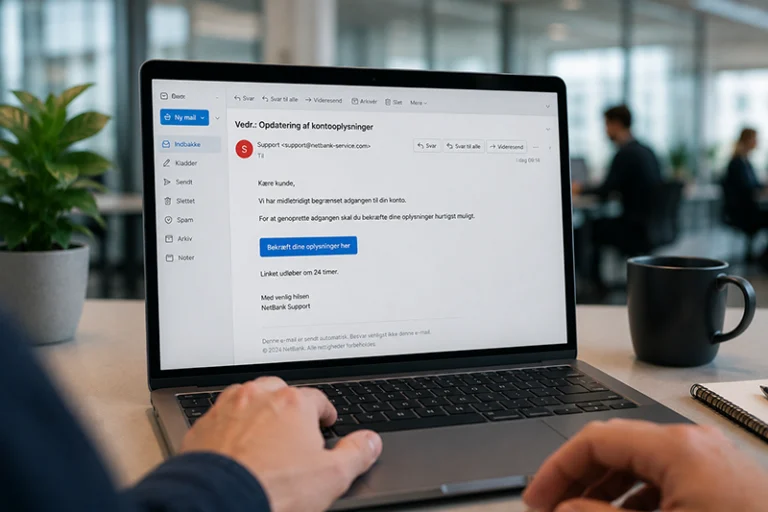
by SecureFirst | Jan 6, 2026 | Blog
NIS2 is not just an IT issue. It is a management responsibility. For the first time, the EU is making it clear that cybersecurity is something that senior management and boards of directors must personally address. This article explains what NIS2 means in practice for management – and how...
by SecureFirst | Jan 6, 2026 | Blog
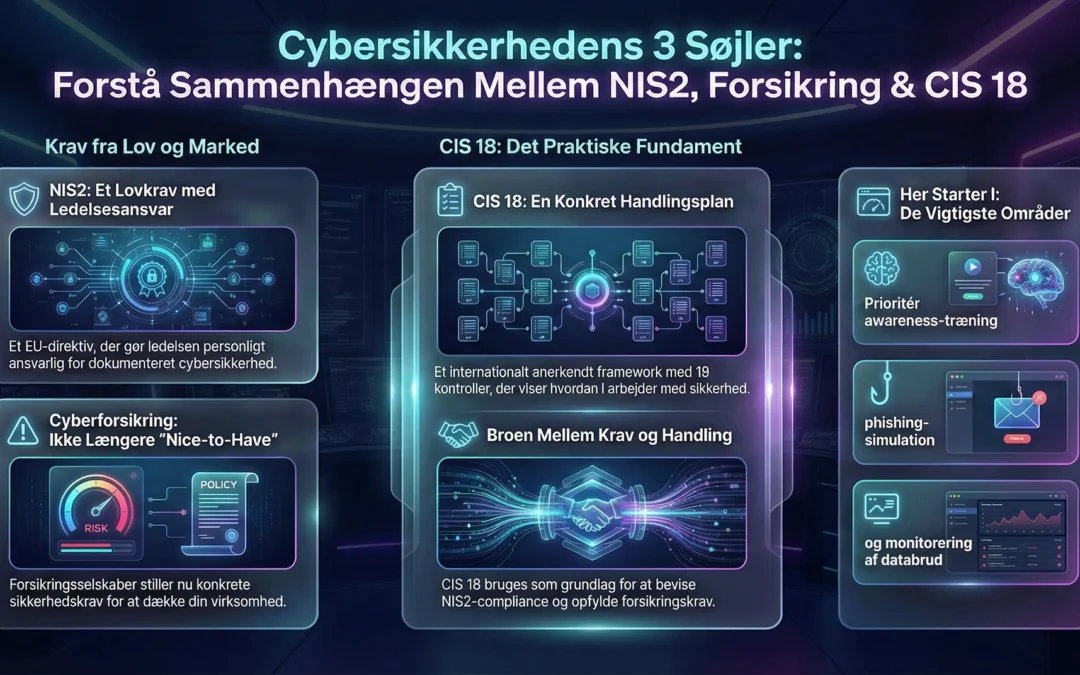
Cybersecurity is no longer a niche technical field. It is a management responsibility, a compliance requirement, and an economic risk factor. This page brings together everything you need to know about: CIS 18 (practical cybersecurity) NIS2 (legislation and responsibility) Cyber insurance (economic risk and...
by SecureFirst | Dec 15, 2025 | Blog
How phishing works and threatens IT security In a digital world where cyber threats are constantly evolving, phishing remains one of the most widespread and dangerous methods hackers use to gain access to sensitive information. Phishing is not only a threat to...
by SecureFirst | Dec 8, 2025 | Blog
Introduction. On February 2, 2025, the initial provisions of the EU's AI Regulation came into effect. This introduces a new legal requirement: all employees who utilize or develop AI must achieve an adequate level of AI Literacy. At SecureFirst, we engage with numerous organizations...
by SecureFirst | Dec 1, 2025 | Blog
Cyber insurance is no longer an option – it's a requirement As cyber threats become increasingly sophisticated and businesses of all sizes are affected by data breaches, ransomware, and phishing, higher demands are placed on corporate cybersecurity. One of the most...
by SecureFirst | Nov 27, 2025 | Blog
Cyber Insurance Requirements Your Business Must Know As digitalization accelerates, the threat of cybercrime becomes increasingly complex and pervasive. Consequently, a growing number of businesses are opting for cyber insurance as a critical security measure. However, many...