NIS2 Compliance Made Concrete and Easy to Understand
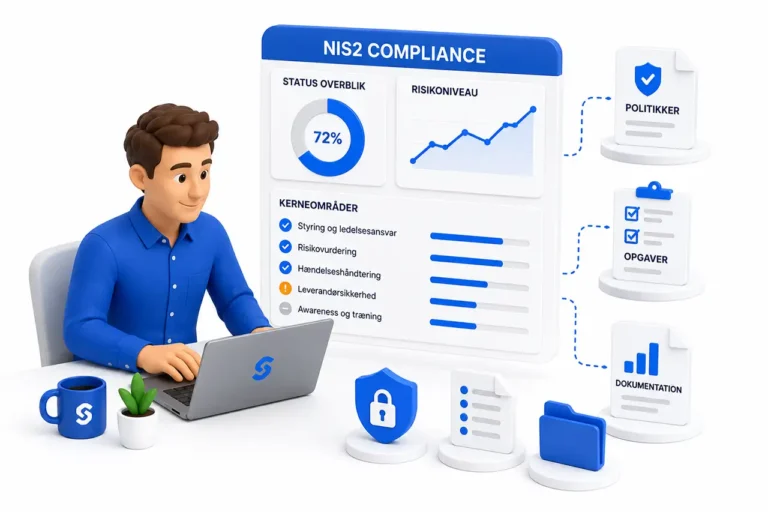
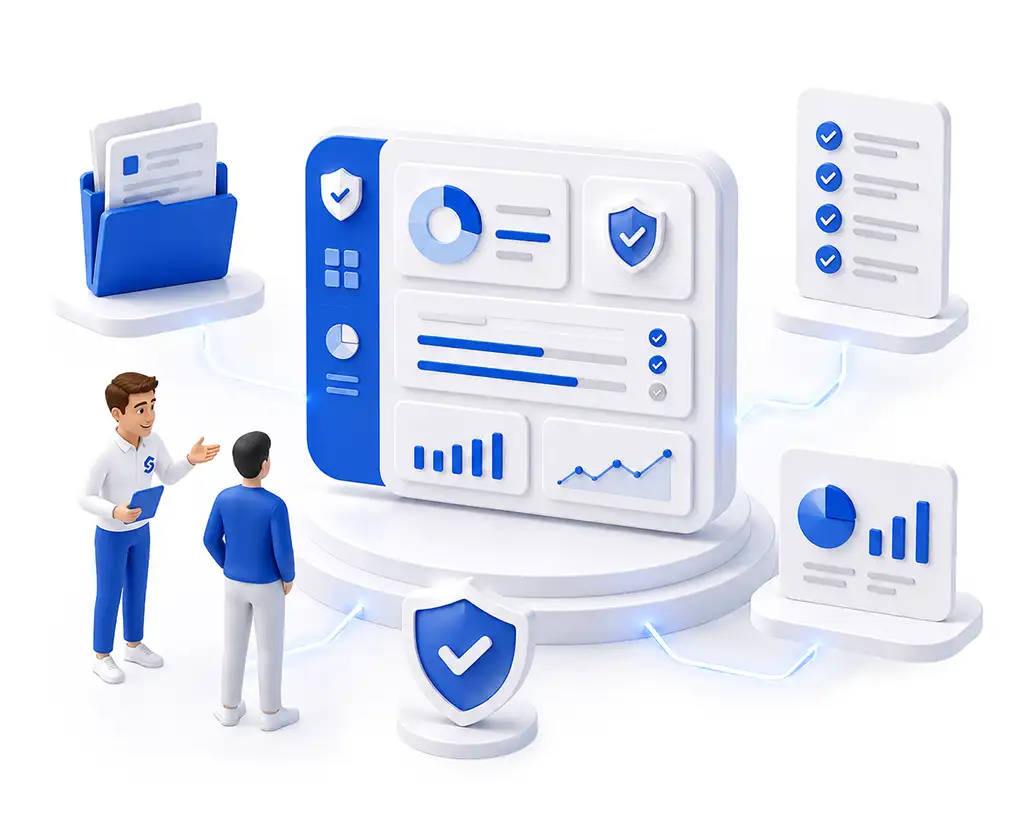
Bring structure to your NIS2 work so that requirements, tasks, and documentation don’t end up scattered across spreadsheets and cumbersome reports. SecureFirst brings together overviews, controls, policies, reporting, and awareness training in a single platform, making it easier for you to prioritize your efforts and demonstrate progress.
Overview of Status, Risks, and Next Steps
Policies, controls, and documentation all in one place
Consulting and onboarding to help you get started in a practical way
See how SecureFirst can help you bring structure to your NIS2 work.






NIS2 may quickly prove difficult to implement in practice
The requirements are clear, but the work is often spread across different systems, documents, and people.
Many companies are well aware that NIS2 imposes stricter requirements regarding security, accountability, documentation, and ongoing monitoring. The challenge arises when these requirements must be translated into concrete actions in day-to-day operations.
It’s not just about policies and documentation. You also need to keep track of controls, risks, responsible parties, suppliers, and employees. When information is scattered across spreadsheets, emails, folders, and various systems, it quickly becomes difficult to maintain an overview.
- Who is responsible for what?
- Which requirements and controls have already been addressed?
- Where are there still gaps or risks?
- Which tasks require action, and from whom?
- How do you document your work and progress over time?
Without a common structure, the NIS2 effort risks becoming an administrative task rather than an active tool for strengthening the organization's security.
This makes it more difficult for IT, management, and compliance to prioritize their efforts, track progress, and document where the organization stands.
From NIS2 Requirements to Practical Next Steps
How to Get Started with NIS2
NIS2 can seem overwhelming if the process begins with long lists of requirements and unclear responsibilities. That’s why we start by getting a clear picture of your current situation and the areas that require action.
With SecureFirst, you get a seamless setup where consulting, the platform, and documentation are integrated from the very beginning.
Step 1 – We assess your current situation
Interviews and Surveys
Onboarding begins with a review of your current situation. This will give you a clearer picture of where things are already under control and where there is a lack of structure, documentation, or action.
The goal is to establish a realistic starting point so that the work doesn't become more extensive than necessary.
Among other things, we’ll look at responsibilities, existing processes, policies, risks, and the documentation you already have. This way, your NIS2 efforts can be based on your actual situation rather than a generic list of requirements.
The assessment provides you with a common foundation for the next steps, so that IT, management, and compliance can prioritize their efforts based on the same overview.


Step 2 – You’ll get a plan for the first steps
Prioritizing Areas of Focus
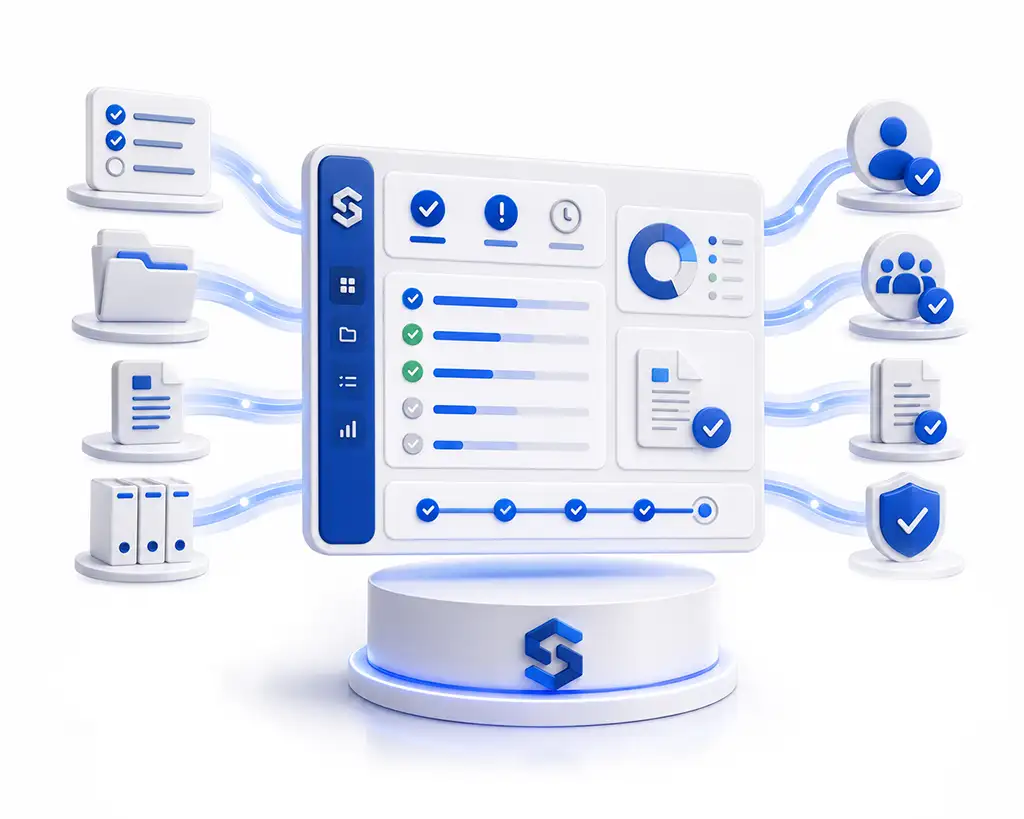
Step 3 – The platform collects assignments and documentation
Overall Overview of Status and Progress
Step 4 – Awareness Becomes Part of the Work
Make NIS2 easy for management and relevant to employees’ daily work
What Customers Say About the Partnership
Get a handle on NIS2 without having to put it all together in a spreadsheet
SecureFirst helps you gain a clear overview, streamline your work, and establish a practical process that’s easy to follow. Below, you can see how other customers rate our collaboration.
-
 Mads
-
Jonas
-
Simon
-
Noah
-
Niklas
-
Malte
-
Sarah
-
Agnes
-
Daniel
-
Ida
-
Alexander
-
Thea
-
Anders
-
Tobias
-
Frederik
-
Trine
-
Julie
-
Laura
-
Caroline
-
Lene
-
Sebastian
-
Signe
-
Camilla
-
Rasmus
-
Sofie
-
Nanna
-
Jesper
-
Annika
-
Alma
-
Louise
-
Mikke
-
Henrik
-
Emilie
-
Oliver
-
Mia
-
Phillip
-
Katrine
-
Kasper
-
Søren
-
William
-
Emma
-
Gustav
-
Maria
-
Viktor
-
Lucas
-
Martin
-
Christian
-
Line
-
Nadia
-
Mads
-
Jonas
-
Simon
-
Noah
-
Niklas
-
Malte
-
Sarah
-
Agnes
-
Daniel
-
Ida
-
Alexander
-
Thea
-
Anders
-
Tobias
-
Frederik
-
Trine
-
Julie
-
Laura
-
Caroline
-
Lene
-
Sebastian
-
Signe
-
Camilla
-
Rasmus
-
Sofie
-
Nanna
-
Jesper
-
Annika
-
Alma
-
Louise
-
Mikke
-
Henrik
-
Emilie
-
Oliver
-
Mia
-
Phillip
-
Katrine
-
Kasper
-
Søren
-
William
-
Emma
-
Gustav
-
Maria
-
Viktor
-
Lucas
-
Martin
-
Christian
-
Line
-
Nadia
-
Sebastian
-
Annika
-
Jesper
-
Gustav
-
Trine
-
Julie
-
Alma
-
Viktor
-
Laura
-
Søren
-
Lene
-
Camilla
-
Ida
-
Nanna
-
Noah
-
Emilie
-
Nadia
-
Mikke
-
Henrik
-
William
-
Oliver
-
Daniel
-
Christian
-
Frederik
-
Agnes
-
Thea
-
Signe
-
Rasmus
-
Maria
-
Martin
-
Lucas
-
Tobias
-
Mia
-
Niklas
-
Jonas
-
Kasper
-
Alexander
-
Louise
-
Mads
-
Line
-
Phillip
-
Anders
-
Caroline
-
Emma
-
Sarah
-
Malte
-
Simon
-
Sofie
-
Katrine
-
Sebastian
-
Annika
-
Jesper
-
Gustav
-
Trine
-
Julie
-
Alma
-
Viktor
-
Laura
-
Søren
-
Lene
-
Camilla
-
Ida
-
Nanna
-
Noah
-
Emilie
-
Nadia
-
Mikke
-
Henrik
-
William
-
Oliver
-
Daniel
-
Christian
-
Frederik
-
Agnes
-
Thea
-
Signe
-
Rasmus
-
Maria
-
Martin
-
Lucas
-
Tobias
-
Mia
-
Niklas
-
Jonas
-
Kasper
-
Alexander
-
Louise
-
Mads
-
Line
-
Phillip
-
Anders
-
Caroline
-
Emma
-
Sarah
-
Malte
-
Simon
-
Sofie
-
Katrine
-
Noah
-
Sarah
-
Daniel
-
Frederik
-
Niklas
-
Sebastian
-
Mads
-
Simon
-
Caroline
-
Nadia
-
Christian
-
Kasper
-
Mikke
-
Jonas
-
Line
-
Viktor
-
Oliver
-
Nanna
-
Louise
-
Lucas
-
Tobias
-
Phillip
-
Lene
-
Emma
-
Katrine
-
Henrik
-
Trine
-
Jesper
-
Laura
-
Søren
-
Alexander
-
Thea
-
Emilie
-
Sofie
-
Alma
-
Ida
-
Rasmus
-
William
-
Mia
-
Camilla
-
Agnes
-
Gustav
-
Signe
-
Anders
-
Maria
-
Martin
-
Malte
-
Julie
-
Annika
-
Noah
-
Sarah
-
Daniel
-
Frederik
-
Niklas
-
Sebastian
-
Mads
-
Simon
-
Caroline
-
Nadia
-
Christian
-
Kasper
-
Mikke
-
Jonas
-
Line
-
Viktor
-
Oliver
-
Nanna
-
Louise
-
Lucas
-
Tobias
-
Phillip
-
Lene
-
Emma
-
Katrine
-
Henrik
-
Trine
-
Jesper
-
Laura
-
Søren
-
Alexander
-
Thea
-
Emilie
-
Sofie
-
Alma
-
Ida
-
Rasmus
-
William
-
Mia
-
Camilla
-
Agnes
-
Gustav
-
Signe
-
Anders
-
Maria
-
Martin
-
Malte
-
Julie
-
Annika
You'll get the price right away!
The Specific Benefits
What do you get with SecureFirst for NIS2?
NIS2 becomes easier to manage when tasks, responsibilities, and documentation are all in one place. SecureFirst helps IT, management, and compliance teams gain a clear overview of their efforts and keep the work moving forward over time.
Bring Your Work Together in One Place
Get an overview of controls, tasks, policies, and documentation without having to manually track the status in multiple files.
Track Progress Over Time
See which areas are in order, where action is needed, and what should be prioritized as the next step.
Make it easier to document the work
Generate reports and compile documentation so you can more easily present the status to management, the board of directors, or relevant stakeholders.
Combine platform and awareness
Support the NIS2 initiative with short awareness training sessions so that employees gain a better understanding of security, responsibility, and cyber hygiene in their daily work.
Try our NIS2 module – without obligation
Link to our privacy policy and terms.
Clients already secured with SecureFirst:


Need clarification?Frequently Asked Questions About NIS2 Compliance
What is NIS2?
NIS2 is the EU’s cybersecurity directive, which imposes stricter requirements on companies and government agencies in critical and key sectors.
Among other things, the directive addresses risk management, security measures, incident reporting, management responsibility, and supply chain security. In practice, this means that organizations subject to the directive must take a more structured approach to cybersecurity and be able to document their efforts.
NIS2 is therefore not just a technical IT project. It requires clearly defined areas of responsibility, up-to-date processes, ongoing monitoring, and employees who understand their role in security efforts.
When must NIS2 be implemented?
The Danish NIS2 Act took effect on July 1, 2025, and affected companies were required to register on virk.dk no later than October 1, 2025.
For organizations subject to NIS2, however, implementation is not just a matter of a single date. The work must be sustainable over time and include risk management, security measures, incident response, documentation, and management oversight.
Therefore, NIS2 should be viewed as an ongoing process in which the company gains an overview of requirements, responsibilities, and progress—and can continuously demonstrate what has been done.
They are more “original content,” less of a summary of the AI Overview, and better at linking the search intent to SecureFirst’s position.
Who is covered by NIS2?
NIS2 covers public and private entities in selected sectors that provide critical or essential societal services. These may include, among others, companies in the energy, transportation, healthcare, digital infrastructure, water supply, food, waste management, public administration, and certain digital services sectors.
Whether a business is covered typically depends on three factors: the sector to which it belongs, the services it provides, and whether it meets the size requirements. However, some entities may be covered regardless of size if they are of particular importance to society.
Therefore, it is not enough to look only at the number of employees or revenue. The company should also assess its role in the supply chain, its customers, and the services it provides.
If you are unsure, you should clarify your status using the official NIS2 check or by contacting the relevant authority. SecureFirst can then help you organize your work by providing an overview, defining responsibilities, managing documentation, and raising awareness.
What are the requirements under NIS2?
NIS2 requires that covered entities systematically address cybersecurity, risk management, management responsibility, incident reporting, and documentation.
The key requirements include registering the company with the authorities, assigning responsibility to management, implementing appropriate security measures, and being able to report significant security incidents. NIS2 also sets requirements for supply chain security, so that companies assess risks associated with relevant business partners and suppliers.
In practice, this means that NIS2 compliance cannot be achieved through technical measures alone. The company must also have clear processes, up-to-date policies, documented follow-up procedures, and employees who understand their role in security efforts.
SecureFirst can help organize your work into a more practical structure, making it easier to manage responsibilities, controls, documentation, and awareness over time.
What does the abbreviation NIS2 stand for?
NIS2 stands for Network and Information Security Directive 2. In Danish, it is often referred to as the Network and Information Security Directive.
NIS2 is the EU’s updated cybersecurity directive and replaces the previous NIS Directive. Its purpose is to establish a higher and more uniform level of cybersecurity in the EU.
In practice, NIS2 means that covered companies and public authorities must adopt a more structured approach to risk management, security measures, incident reporting, management responsibility, and documentation.