CIS18 Compliance: Overview, Prioritization, and Documentation
CIS18 provides a concrete framework for strengthening an organization’s cybersecurity. The challenge arises when controls, policies, tasks, and documentation must be translated into a process that IT, management, and the rest of the organization can implement.
Get an overview of the status and gaps in your CIS18 controls
Prioritize quick wins using gap analysis and specific next steps
Bring together policies, tasks, and documentation in one place
Track progress with reports ready for management and the board of directors
Learn how SecureFirst can make CIS18 easier to implement in practice.






CIS18 can be difficult to translate into specific tasks
CIS18 provides a clear safety framework, but the work only becomes valuable when the controls are linked to accountability, prioritization, and documentation.
Many companies would like to take a more systematic approach to cybersecurity, but it can be unclear where to start and how to prioritize these efforts.
- Which checks are most important right now?
- Where is the documentation missing?
- How do we demonstrate progress over time?
Without a comprehensive overview, CIS18 efforts can quickly devolve into spreadsheets, ad hoc policies, and manual status updates. This makes it difficult for IT to prioritize efforts and for management to see how security efforts are progressing.
It can also make it difficult to keep the work moving forward after the initial review. When tasks, checks, and documentation are scattered, CIS18 becomes a cumbersome framework to implement in practice.
That is why companies need a simple way to consolidate work, track progress, and drive momentum across the organization.
From Overview to Prioritized Action
How to Get Started with CIS18
CIS18 is most valuable when the controls are not merely reviewed once, but are translated into specific tasks, priorities, and ongoing follow-up.
SecureFirst helps you establish a practical starting point so you can see where you stand today, which areas require action, and how your progress can be documented over time.
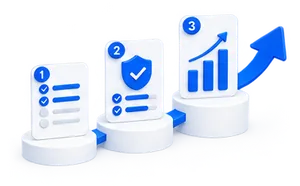
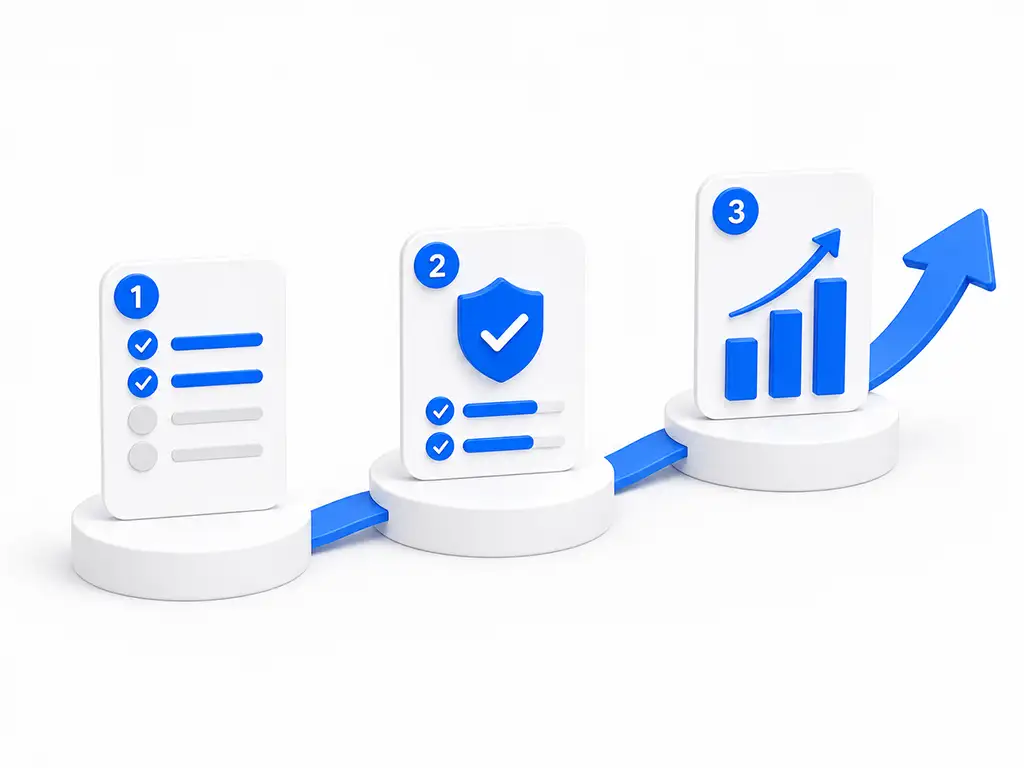
Step 1
Assess your current level of security
The first step is to get an overview of how the company currently implements the relevant CIS18 controls.
Here, you’ll identify both what’s already working well and the areas where there’s a lack of structure, documentation, or follow-up.
The assessment provides IT and management with a shared understanding of the security level, so that their work can be based on facts rather than assumptions.

Step 2
Prioritize the most important gaps
Step 3
Track progress and document the work
Here's what you get with SecureFirst for CIS18
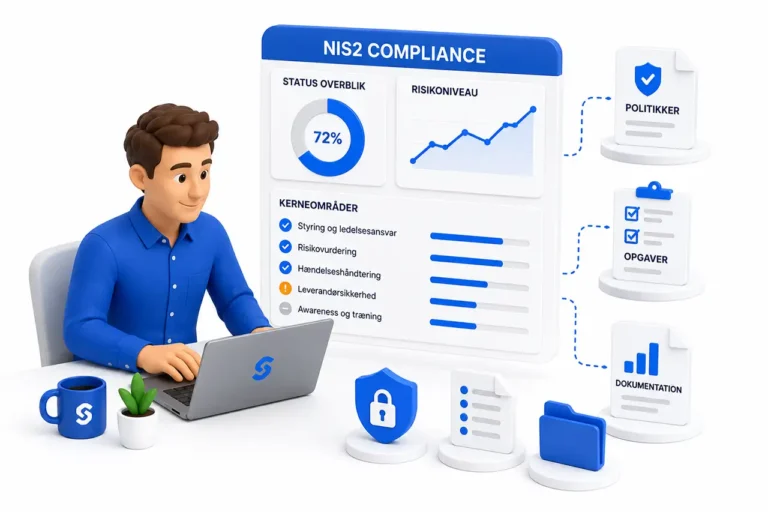
Dashboard with Status and Progress
SecureFirst makes it easier to implement CIS18 in practice because the platform brings together the most important aspects of security work in one place. This gives IT a better foundation for prioritizing efforts, tracking progress, and documenting work over time.
Gap Analysis of Your Security Level
Get a clear picture of where your current security efforts stand in relation to CIS18.
Advantage:
You can see which areas are already well covered and where improvements are needed.
Policies and documentation all in one place
Gather relevant policies, processes, and documentation so they aren't scattered across folders, emails, and spreadsheets.
Advantage:
It becomes easier to maintain safety procedures and locate documentation when needed.
Reporting to Management and Stakeholders
Generate reports that show status, progress, and areas of focus.
Benefit:
You’ll have a stronger foundation for dialogue with management, the board of directors, customers, or other stakeholders.
Awareness as Part of Safety Efforts
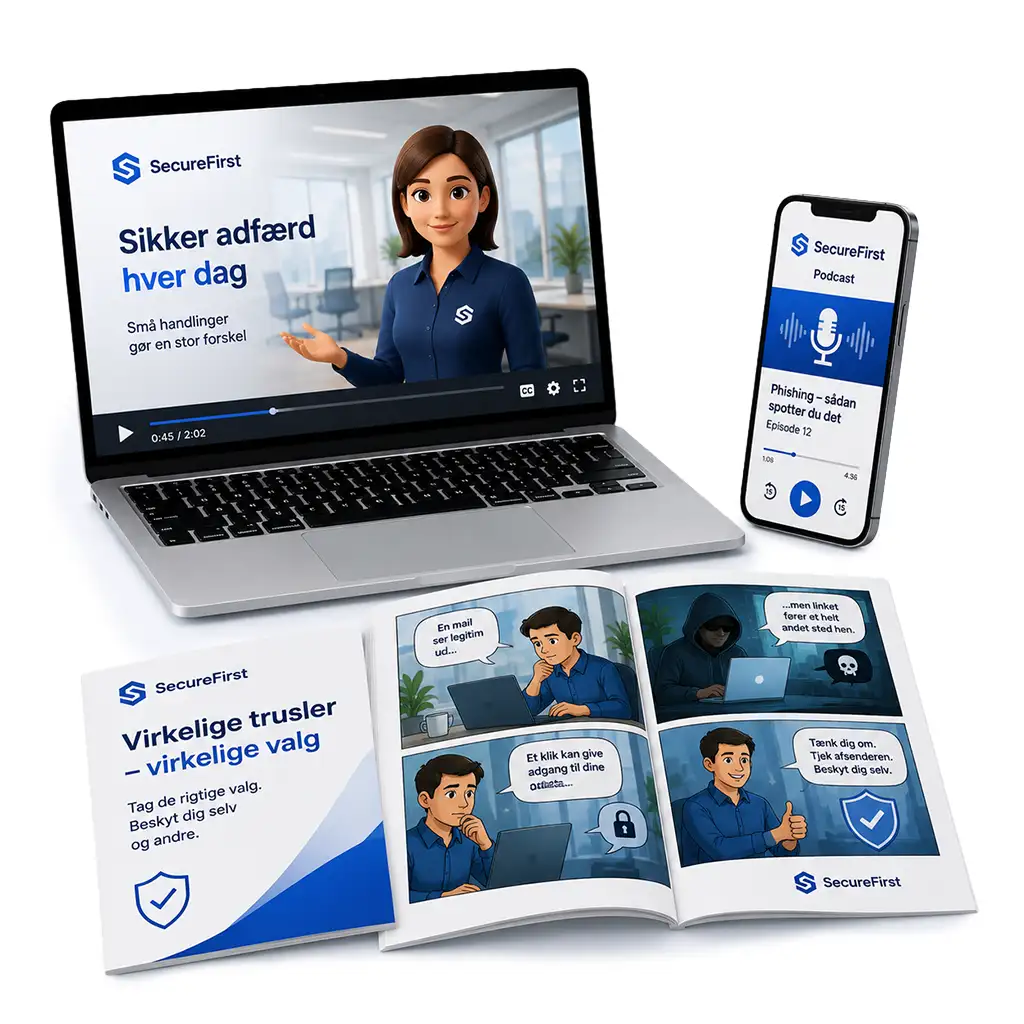
Combine the CIS18 initiative with short awareness programs that make security more tangible for employees.
Benefit:
Security efforts become not just an IT project, but an integral part of the organization’s day-to-day operations.
Try our CIS18 module – no commitment required
Link to our privacy policy and terms.
Clients already secured with SecureFirst:


Need clarification?What other companies have asked
What is CIS18 – and why is it relevant?
An international framework comprising 18 control areas and 153 recommendations, providing a
structured, prioritized path to enhanced cybersecurity and simplified documentation.
Is CIS18 a legal requirement?
No, but it supports requirements and expectations from, for example, NIS2, GDPR, clients, and
cyber insurance – providing a solid foundation for compliance.
What level do we start at (Implementation Groups)?
CIS18 is divided into IG1, IG2, and IG3. We assess your organization's size, risk profile, and maturity, and
recommend a starting level – with the flexibility to expand continuously.
How do we get started?
We begin with an introductory meeting. Subsequently, we conduct onboarding with a joint gap analysis
and a plan for “quick wins” and next steps. You gain access to the platform on the same day.
How long does it take to become compliant?
This depends on your starting point. You will achieve rapid results (quick wins) within a few weeks and a roadmap for full implementation over several months – with ongoing status updates.
What if we already have policies and controls in place?
We map existing material to CIS18, leverage effective components, and focus solely on the gaps. This eliminates redundant efforts.
How does AI provide practical assistance?
AI facilitates clear reports, policy/process proposals, and comprehensible status summaries, empowering both IT and management to act promptly and securely.
How are policies and processes managed throughout the year?
The platform offers templates, assigns responsibilities and due dates, and provides review reminders, ensuring governance is maintained efficiently without becoming burdensome.
Can documentation be provided to management, the board, and auditors?
Yes. You will receive dashboards and exportable reports that highlight new risks, implemented improvements, and supporting evidence – providing audit-ready documentation.
Does this provide assistance concerning customers, authorities, and cyber insurance?
Yes. The output can be directly leveraged for due diligence, questionnaires, and requirements from insurance providers – thereby mitigating friction in communication.
What if progress is hindered or time constraints arise?
Consultant support is included. You can schedule our cybersecurity specialists directly within the platform, ensuring continuous assistance.
What are the costs?
Fixed monthly pricing with no hidden fees. (Utilize our price calculator or contact us for a tailored quote.)